For security & compliance review

Secure AI for the work that matters most in the boardroom.

Helping Chairs, committees and directors reduce repetitive work, stay aligned and make better decisions, with deeper intelligence from your own materials, market signals, Scenario Analysis and Tabletop Exercises. Built for the confidentiality, accountability and governance standards board work requires.
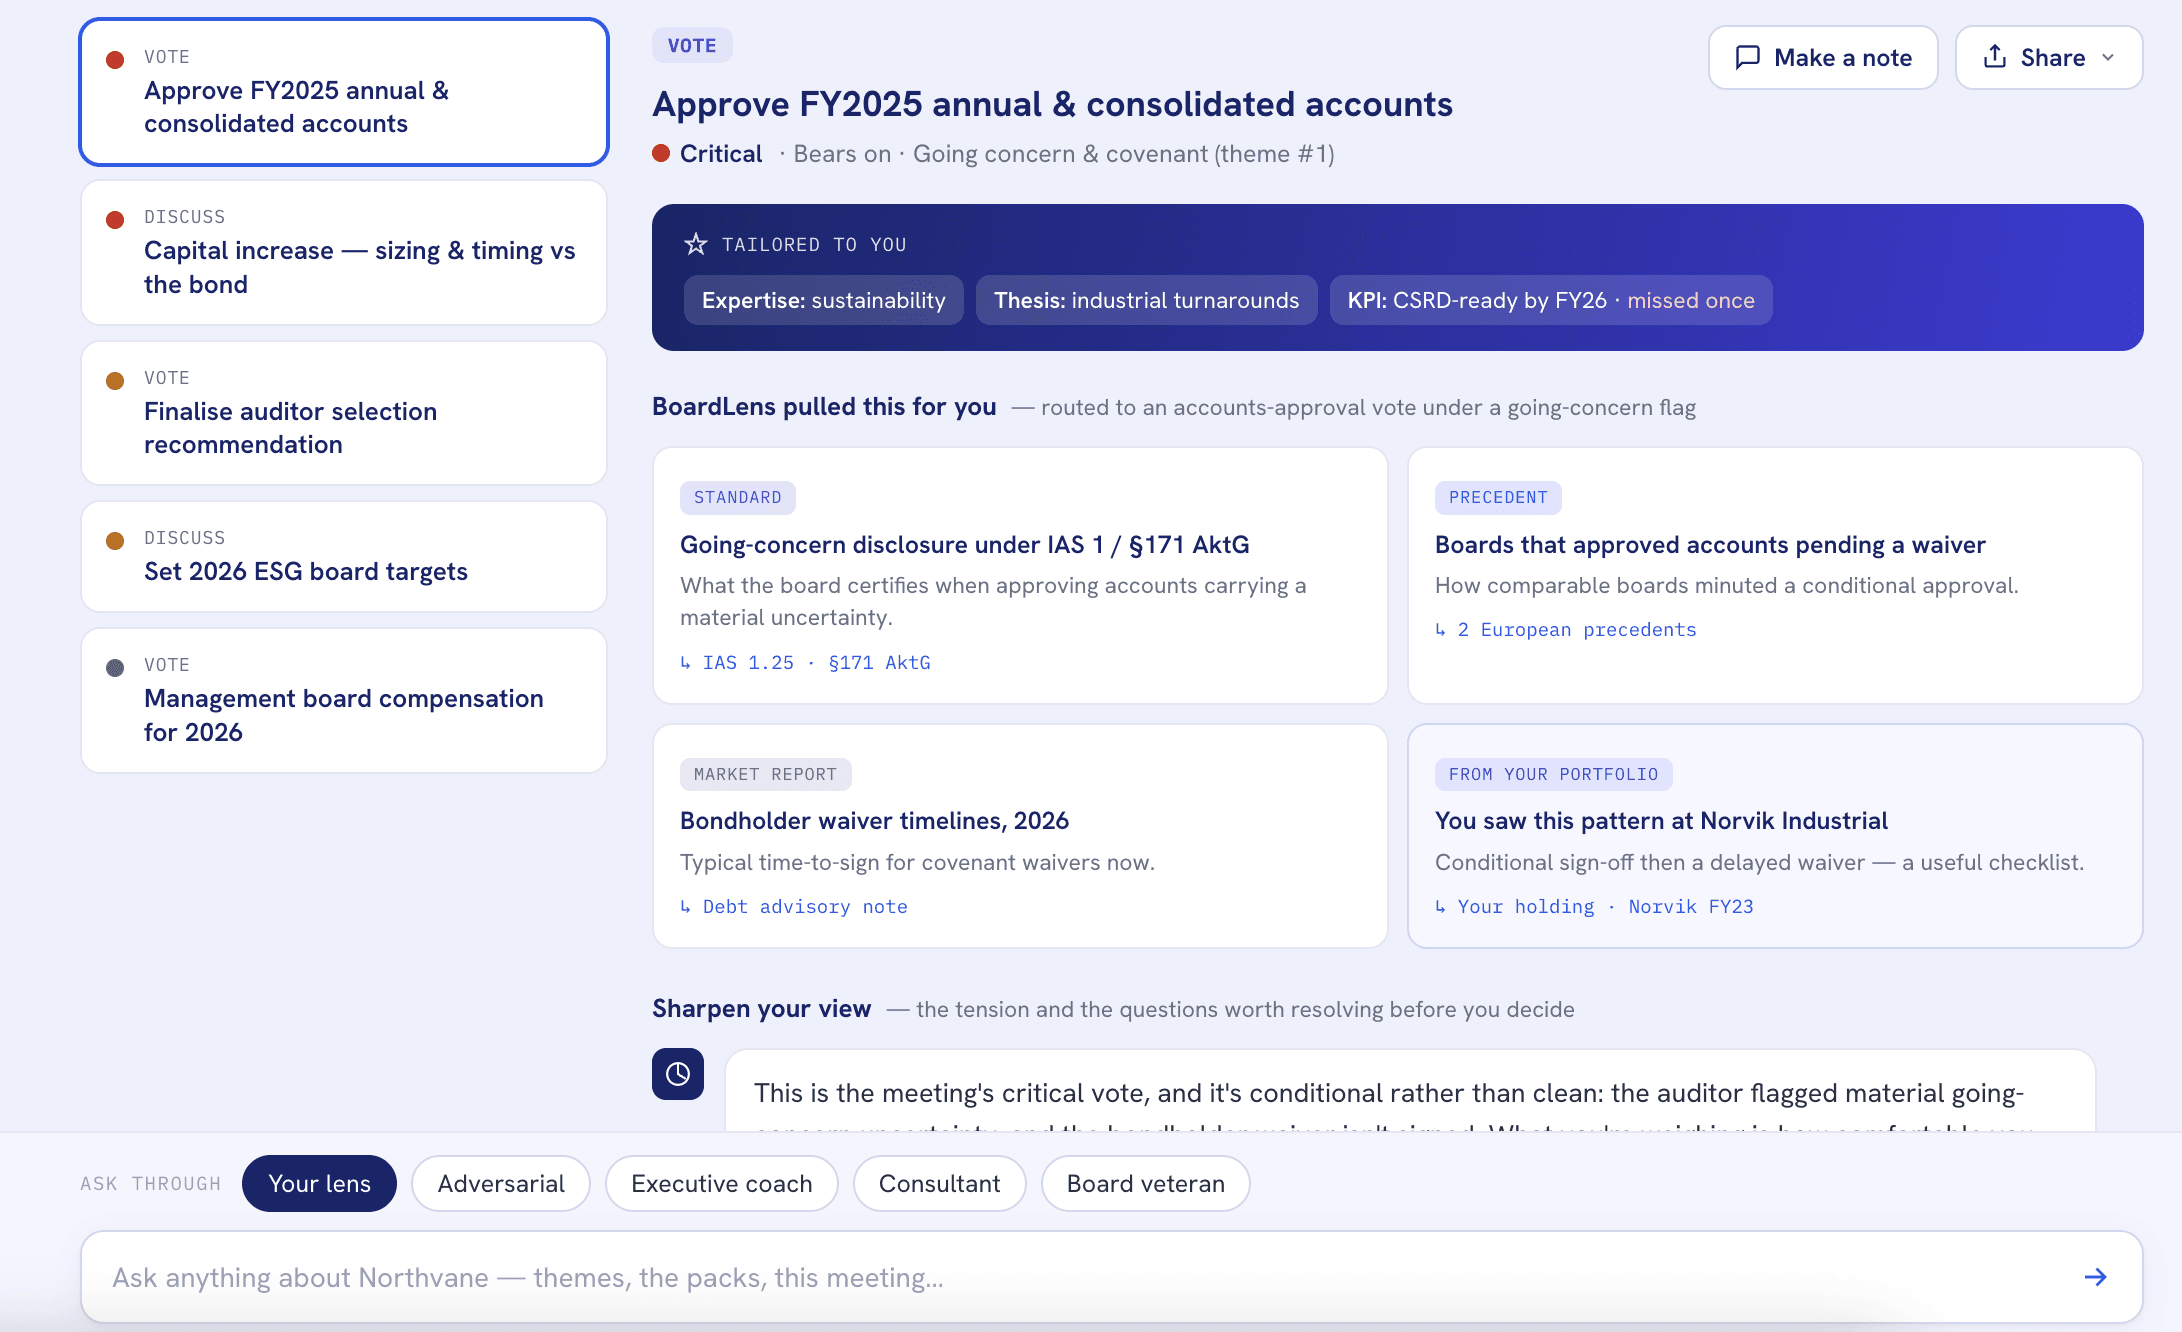
BoardLens product view showing a board decision with supporting evidence and director perspectives
  • Never trained on your data
  • EU data residency (Frankfurt)
  • SOC 2 audit-ready, monitored daily
  • GDPR compliant

Governance for the AI era

A workspace for modern board work.

BoardLens gives boards a secure way to use AI across more of the work they already do.

Automate the tedious work around boards and committees

Reduce repetitive preparation, agenda building, minutes and follow-up.

See important changes earlier

Connect current materials with prior decisions, commitments and relevant external developments.

Keep boards and committees aligned

Maintain continuity across the Main Board, committees, meetings, projects and delegated work.

Test the assumptions behind important decisions

Use Scenario Analysis to explore what changes under different assumptions and what remains robust.

Rehearse high-stakes situations before they become real

Use Tabletop Exercises for cyber incidents, CEO transitions, activist approaches and strategic disruption.

See the company the way an activist would before an activist does

Challenge the narrative, surface contradictions and understand where an external critic could make the strongest case.

The shadow AI problem

AI is already in the boardroom.

The question is no longer whether directors will use AI. It is whether sensitive board information is handled in a sanctioned environment built for the confidentiality, accountability and governance standards board work requires.

82%

of directors say they've used generative AI in their board work in the past six months.

54%

say their company gives them no guidance on how to do it safely.

Source: Diligent Institute.

“At Tallence, both our executives and board members use BoardLens together. It's become our shared platform for stronger strategic conversations and better-prepared board meetings.”
Wolf-Ingomar FaecksWolf-Ingomar FaecksChairman of the Supervisory Board, Tallence AG

An overview for your board and stakeholders

Download a concise overview of BoardLens, what it does and how it is designed for secure board-wide use.

  • For your Chair and board
  • For legal, compliance and security teams
  • For procurement
  • For internal stakeholders
Download the overview (PDF)

BoardLens Trust Center

Review our security controls, compliance documentation, subprocessors and supporting evidence.

  • Security and privacy documentation
  • Subprocessors
  • Compliance and assurance
  • Policies and governance
Visit Trust Center

Security & compliance at a glance

Your data stays yours.

Learn more about our security approach

BoardLens is built for sensitive board information, with enterprise-grade security, clear provenance and governance controls.

  • Never trained on your data
  • EU data residency (Frankfurt)
  • SOC 2 audit-ready, monitored daily
  • Encryption in transit and at rest
  • Tenant isolation
  • You control who can access each workspace

Security questions, answered

FAQ

View all FAQs
Do you train AI models on our board materials?
No. Never. Every AI provider we use is bound by a signed data processing agreement with an explicit no-training commitment. Your data is used to answer your questions, nothing else. Your compliance team can review every one of these contracts in our Trust Center.
Where is our data stored?
All customer data is stored in AWS in Frankfurt, Germany, encrypted at rest with dedicated keys and in transit via TLS. Nothing is stored on laptops, file-sharing tools or third-party services. AI providers process queries under the data processing agreements above and do not retain your documents.
Which AI providers do you use?
Every AI provider we use (Anthropic, OpenAI, Google, Mistral) is bound by a signed data processing agreement with an explicit no-training commitment. Your data is used to answer your questions, nothing else. Your compliance team can review every one of these contracts in our Trust Center.
How is our data separated from other customers?
Every record in our database is bound to your organization's tenant ID at the schema level, and every query is scoped to that ID by the application, without exception. Isolation is also enforced by the database itself through row-level security, independently of application code. One board's data can never appear in another board's results. This isolation is one of the controls monitored daily as part of our SOC 2 program.
Who can see our board information?
You control who can access each workspace, and can delete it whenever you choose. Invite directors with roles, control per-company access, distribute the deck, share briefs securely.
Are you SOC 2 compliant?
Our SOC 2 program reached 100 percent control readiness in July 2026 and we are now in the formal audit observation window with the independent attestation report expected in October 2026. In the meantime our systems are monitored continuously by Drata, an independent compliance platform, and you can see our live control status in the Trust Center.
Are you GDPR compliant?
BoardLens was built for GDPR from the start: records of processing, a data protection impact assessment for document analysis, data subject rights procedures, a breach notification procedure, and a transfers register covering every US subprocessor. All documentation is available for review.
What happens if the AI produces an unsupported claim?
This is the core of how BoardLens is engineered. Every factual claim must carry a citation to a specific document and page, enforced at the database level. Click any claim and the source page opens next to it. Outputs that fail validation get one automated correction attempt and are otherwise rejected, never silently shown. Every release is gated on automated citation verification against a regression test set, and output quality is judged by an AI from a different vendor, so no model evaluates its own work.
Can we review your subprocessors and DPAs?
Yes, that is the point. Our Trust Center gives your IT, security or compliance team direct access to our subprocessor contracts, live compliance monitoring status and security documentation. Do not take our word for anything.
Can we delete our data?
Customers can also irreversibly delete their data at any time.

Have a question?

We’re here to support your review.

Our team is happy to work directly with your security, legal or compliance team and provide the information you need.